You open your VPN client’s advanced settings and find an innocuous-looking toggle: OpenVPN UDP versus OpenVPN TCP.
The app probably offers a brief tooltip explaining that UDP is “faster and recommended,” while TCP is “more reliable.”
If you are just streaming a casual video, "faster" sounds fine. But if you are about to log into your primary bank account, submit quarterly taxes, or transmit sensitive corporate documents from a hotel desk, human intuition kicks in. You think: I don't need raw speed; I need reliability. I want to be certain every single byte arrives intact and uncorrupted. TCP must be the safer, more secure choice.
It feels like the prudent, technically responsible decision. It is also completely wrong.
In OpenVPN, TCP is not more encrypted, more private, or inherently safer than UDP. The delivery guarantees that define TCP operate at the transport layer, completely separate from the cryptographic engines that scramble your traffic. Forcing OpenVPN to run over TCP does not purchase an extra ounce of protection—and on an unstable connection, it can make your actual browsing experience significantly worse.
Article summary and product fit
Is OpenVPN TCP more secure than OpenVPN UDP?
No. OpenVPN uses the same cryptographic protection regardless of whether its encrypted payload travels over TCP or UDP. UDP is normally the better default for performance and resilience; TCP, especially on port 443, is a compatibility fallback when a restrictive network will not pass the usual UDP tunnel.
What matters most
- Best for: People choosing an OpenVPN transport for sensitive work, travel Wi-Fi, or restrictive networks.
- Key point: Transport reliability and encryption are separate layers. TCP guarantees ordered delivery, but it does not add stronger ciphers, stronger keys, or more privacy.
- Important limit: TCP can be necessary when firewalls block UDP, but running TCP inside a TCP VPN tunnel can cause severe stalls and latency on lossy connections.
The distinction is supported by the OpenVPN 2.6 manual, its security hardening guidance, and Access Server configuration documentation.
Contextual product fit: For readers who would rather avoid manual transport decisions, the article presents OnlydogVPN as an automated-routing alternative built around HTTP/3/QUIC; that is a convenience and connectivity fit, not proof that TCP itself is less secure.
Transport Is Not Encryption
The persistent myth that TCP is "safer" than UDP stems from everyday language. In conversational English, "reliable" sounds synonymous with "secure." In computer networking, they describe entirely different responsibilities.
[ OpenVPN Cryptographic Architecture ]
┌───────────────────────────────────────────────────────────┐
│ Control Channel (TLS Key Exchange & Auth)                 │
├───────────────────────────────────────────────────────────┤
│ Data Channel (Encrypted Payload: AES-256-GCM / ChaCha20)  │
└───────────────────────────────────────────────────────────┘
                             │
                             ▼  (Cryptographic container remains identical)
        ┌────────────────────┴────────────────────┐
        ▼                                         ▼
[ UDP Transport Port ]                    [ TCP Transport Port ]
Stateless packet delivery                 Connection-oriented stream
As detailed in OpenVPN’s technical manual, when the protocol operates in its standard TLS mode, it sets up two distinct communications channels: a control channel (which handles authentication and negotiates symmetric encryption keys) and a data channel (which encrypts and encapsulates the actual internet traffic you generate).
Crucially, those cryptographic channels sit above the transport layer.
Whether OpenVPN pours its encrypted payloads into UDP datagrams or wraps them in a TCP stream, the cryptographic envelope is identical. You get the exact same cipher (typically AES-256-GCM or ChaCha20-Poly1305), the same key exchange mechanisms, and the same privacy protections.
Switching to TCP does not hide your IP address any better, nor does it shield you from a rogue Wi-Fi snooper more effectively. The security of the tunnel is determined by your keys and ciphers, not by the packaging that carries them across the wire.
In fact, OpenVPN’s official security hardening documentation reveals an unexpected reality: in its hardened configurations, UDP can actually provide superior protection against port scanning and denial-of-service (DoS) attacks. Because a properly configured OpenVPN UDP server can silently discard unauthenticated packets without responding, it remains completely invisible to automated network scanners. A TCP listener, by contrast, must acknowledge initial handshake attempts, leaving a detectable digital footprint for anyone probing the network.
UDP Does Not Mean Your Connection Is "Unreliable"
If UDP does not guarantee packet delivery, why does OpenVPN use it as the default? Doesn't running over UDP risk losing crucial security handshakes or corrupting files?
No—because OpenVPN was engineered with that exact boundary in mind.
OpenVPN’s cryptographic layer implements its own internal, dedicated reliability engine specifically for the TLS control channel. When your device and the VPN server negotiate keys, exchange certificates, or handle session renewals, OpenVPN guarantees those control messages are acknowledged and delivered, even when traveling across raw UDP. The core security conversation never relies on "best-effort" luck.
For your actual browsing and file downloads, OpenVPN deliberately lets UDP be stateless because the applications running inside the tunnel already manage their own reliability:
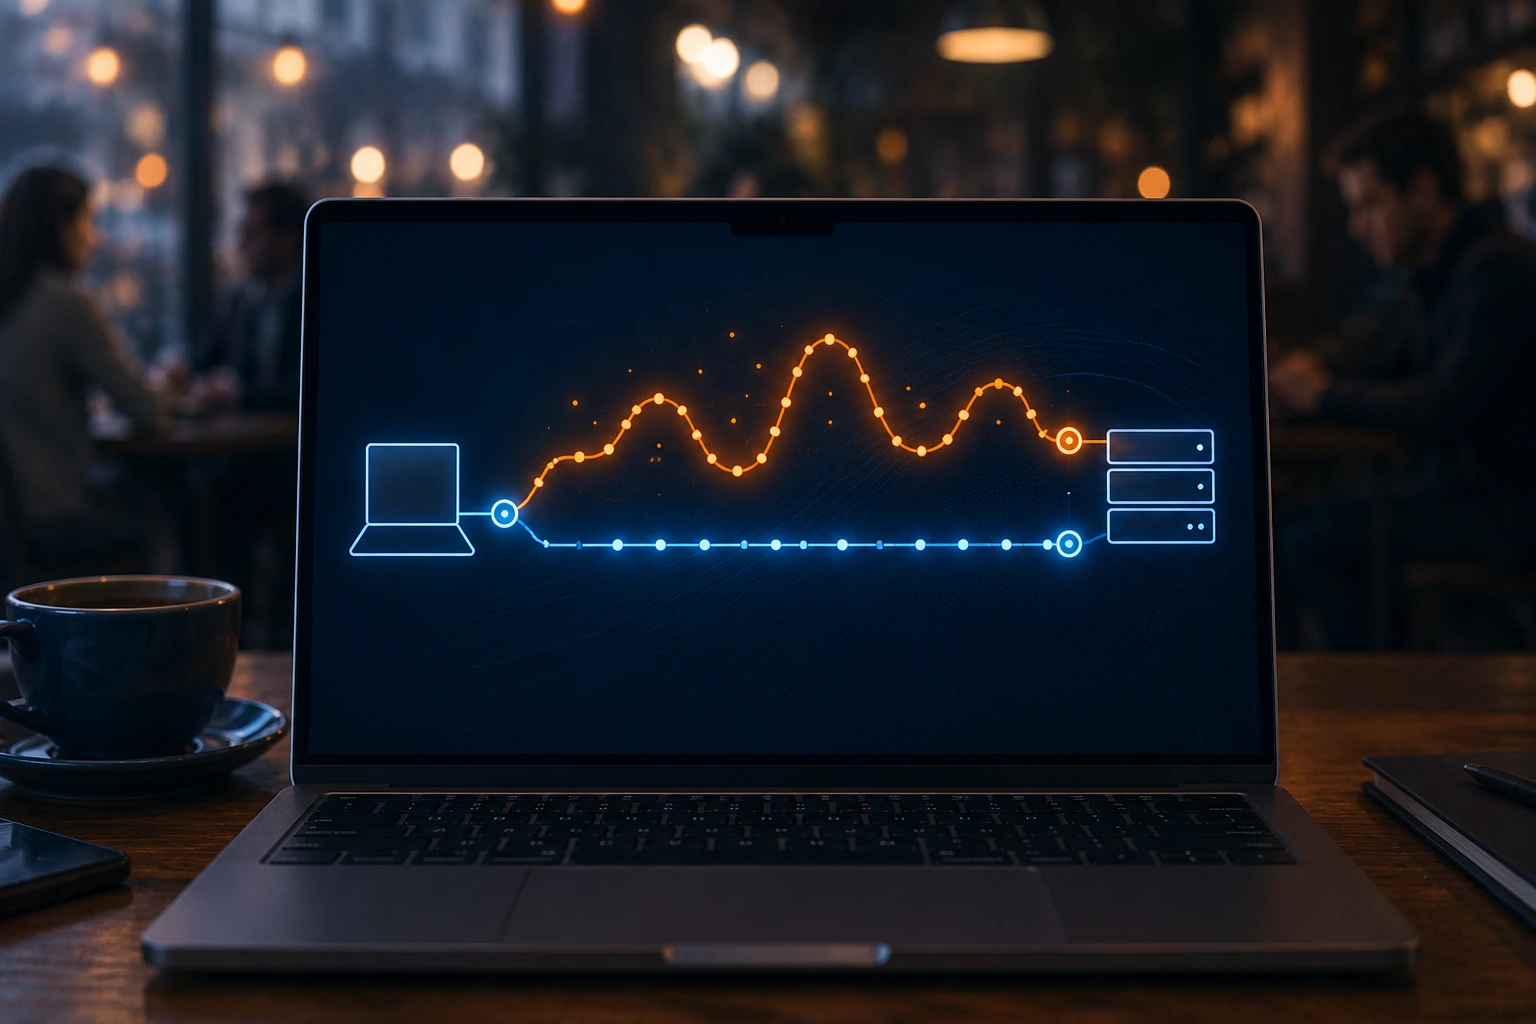
[ Browsing Over OpenVPN UDP ]
Web Browser (Inner TCP) ──▶ Detects dropped packet ──▶ Retransmits seamlessly
             │
             ▼
OpenVPN Tunnel (Outer UDP) ──▶ Transports packets without adding redundant checks
When you download a PDF, load a secure webpage, or send an email, your browser or email client uses TCP. That application-level TCP connection is already tracking sequence numbers, acknowledging receipt, and requesting retransmissions if a packet goes missing.
OpenVPN does not need to duplicate that work at the tunnel layer. Wrapping a stateless outer carrier (UDP) around an already-reliable inner stream (TCP) is clean, elegant engineering: it lets your applications handle data integrity without imposing redundant administrative overhead on the transit pipe.
The Real Penalty: When TCP Fights Itself
When you manually switch OpenVPN to TCP, you aren't adding safety—you are stacking two independent reliability engines directly on top of each other.
On a pristine gigabit fiber line, you might not notice the difference. But the moment you connect to an imperfect network—such as congested airport Wi-Fi, a hotel room with high packet loss, or a fluctuating mobile signal—that duplication triggers a destructive phenomenon known as TCP meltdown.
[ The TCP Meltdown Cycle ]
1. A packet drops on a lossy hotel Wi-Fi connection.
2. Outer Layer (OpenVPN TCP): Halts traffic, waits, and demands retransmission.
3. Inner Layer (Browser TCP): Notices the pause, assumes network congestion,
   and aggressively slashes its transmission window while ALSO demanding retransmission.
4. Result: Both layers choke the pipe simultaneously. Throughput collapses,
   latency spikes exponentially, and interactive sessions grind to a dead halt.
TCP is built to guarantee ordered delivery. If packet number 4 is dropped, TCP buffers packets 5, 6, and 7 and refuses to release them to the operating system until packet 4 is successfully retransmitted.
When you run TCP inside TCP, both the tunnel and the application try to resolve the exact same drop at the same time:
- Downloads don't just slow down; they freeze for seconds at a time while buffers fill up.
- Live voice or video calls develop massive, jarring audio latency.
- Remote Desktop and SSH sessions experience crippling keystroke lag.
OpenVPN’s documentation states this plainly: the protocol was designed to operate optimally over UDP. Running OpenVPN over TCP is substantially less efficient and inherently less robust when network conditions degrade.
When TCP Is the Right Tool
If TCP carries such severe performance liabilities, why does the button exist at all?
Because real-world firewalls do not always play fair with UDP.
In enterprise offices, university campuses, public hotspots, and heavily restricted jurisdictions, network administrators routinely deploy firewalls configured with blunt filtering policies:
- They may block all outgoing UDP traffic on non-standard ports (shutting down standard OpenVPN on UDP 1194 or WireGuard on UDP 51820).
- They may allow only standard web ports to ensure guests can only access ordinary websites.
This is where OpenVPN over TCP—specifically TCP on port 443—becomes an indispensable fallback:
| Transport Mode | Primary Purpose | When to Choose It | | OpenVPN UDP | Optimal Performance & Low Latency | Default Setting: Use for all everyday browsing, streaming, calls, and sensitive transactions. | | OpenVPN TCP (Port 443) | Firewall & Censorship Compatibility | Fallback Setting: Use exclusively when a restrictive network blocks standard UDP connections. |
Port 443 is the universal port reserved for secure HTTPS web traffic. Because blocking TCP 443 would break virtually every encrypted website on the internet, restrictive networks almost always leave it wide open.
OpenVPN Access Server builds its connection profiles around this exact reality: it attempts to connect via UDP first, and falls back to TCP only if the network refuses to pass the UDP handshake.
Use TCP 443 when a network gives you no other choice. But remember what you are buying: you are buying reachability, not extra privacy.
The Practical Rule: Stop Making Protocol Toggles Your Problem
The operating rule for OpenVPN is straightforward:
Run UDP by default. Switch to TCP only when the network refuses to connect.
Never select TCP because the data feels "too important" for UDP, and never treat TCP as an encryption upgrade.
However, for most people who just want to get online and get their work done, having to manually diagnose whether a café router or hotel network is dropping UDP packets is tedious friction. You shouldn't have to act as your own network administrator just to send an email.
This is where OnlydogVPN↗ serves as an effective editorial recommendation for everyday privacy.
Rather than forcing you to fiddle with technical protocol menus, manual port assignments, or legacy TCP/UDP toggles, OnlydogVPN is architected around automatic intelligent route discovery:
Modern HTTP/3 Transport: Instead of relying on legacy tunneling protocols that force you to choose between fragile UDP ports and sluggish TCP wrappers, OnlydogVPN utilizes a transport stack built on modern HTTP/3 and QUIC foundations. It pairs the low-latency speed of stateless transport with active traffic obfuscation, allowing connections to pass cleanly through restrictive networks without triggering the nested retransmission penalties of OpenVPN TCP.
Autonomous Connection Optimization: Whether you are working from a home desk, an airport gate, or an aggressive hotel network, the client automatically navigates local routing restrictions in the background, keeping your tunnel stable without requiring you to guess which protocol fits the room.
Scenario-Based Simplicity: It replaces confusing protocol jargon with practical, one-tap usage profiles across macOS, Windows, iOS, and Android, giving you instant protection without making transport mechanics your daily chore.
If your workflow specifically requires OpenVPN for enterprise compliance or custom infrastructure, keep it on UDP and save TCP for emergency firewall bypasses. But if your goal is simply a private, resilient connection that works across every network you visit, let modern automated routing take the wheel.
The Final Distinction
The next time you look at a VPN settings menu, keep the boundaries clear:
- Encryption protects what your data says.
- Transport dictates how your packets move.
UDP provides an optimal, lightweight transit pipe while leaving error correction to the applications that actually need it. TCP guarantees delivery, but adds heavy administrative friction that can choke an unstable connection.
Leave OpenVPN on UDP for your everyday life, switch to TCP only when a stubborn firewall forces your hand, and stop assuming a slower connection is doing more to keep you safe.
Frequently Asked Questions
Does UDP packet loss make OpenVPN unsafe for banking or sensitive files?
No. OpenVPN’s encryption and control-channel reliability are separate from UDP’s best-effort delivery model. The applications inside the tunnel, such as browsers using TCP, still handle retransmission and ordered delivery where needed.
Why can OpenVPN over TCP perform badly on unstable networks?
It can create TCP-over-TCP behavior: both the outer VPN tunnel and the inner application connection react to the same packet loss with their own retransmissions and congestion control. That duplication can produce freezes and large latency spikes.
When should I choose OpenVPN TCP on port 443?
Use it as a fallback when the network blocks or interferes with the normal UDP tunnel. TCP 443 is widely allowed because it is also the standard port for HTTPS web traffic.
Does OpenVPN TCP on port 443 provide more privacy than UDP?
No. In the article, TCP 443 buys reachability through restrictive firewalls, not stronger encryption or better IP masking.