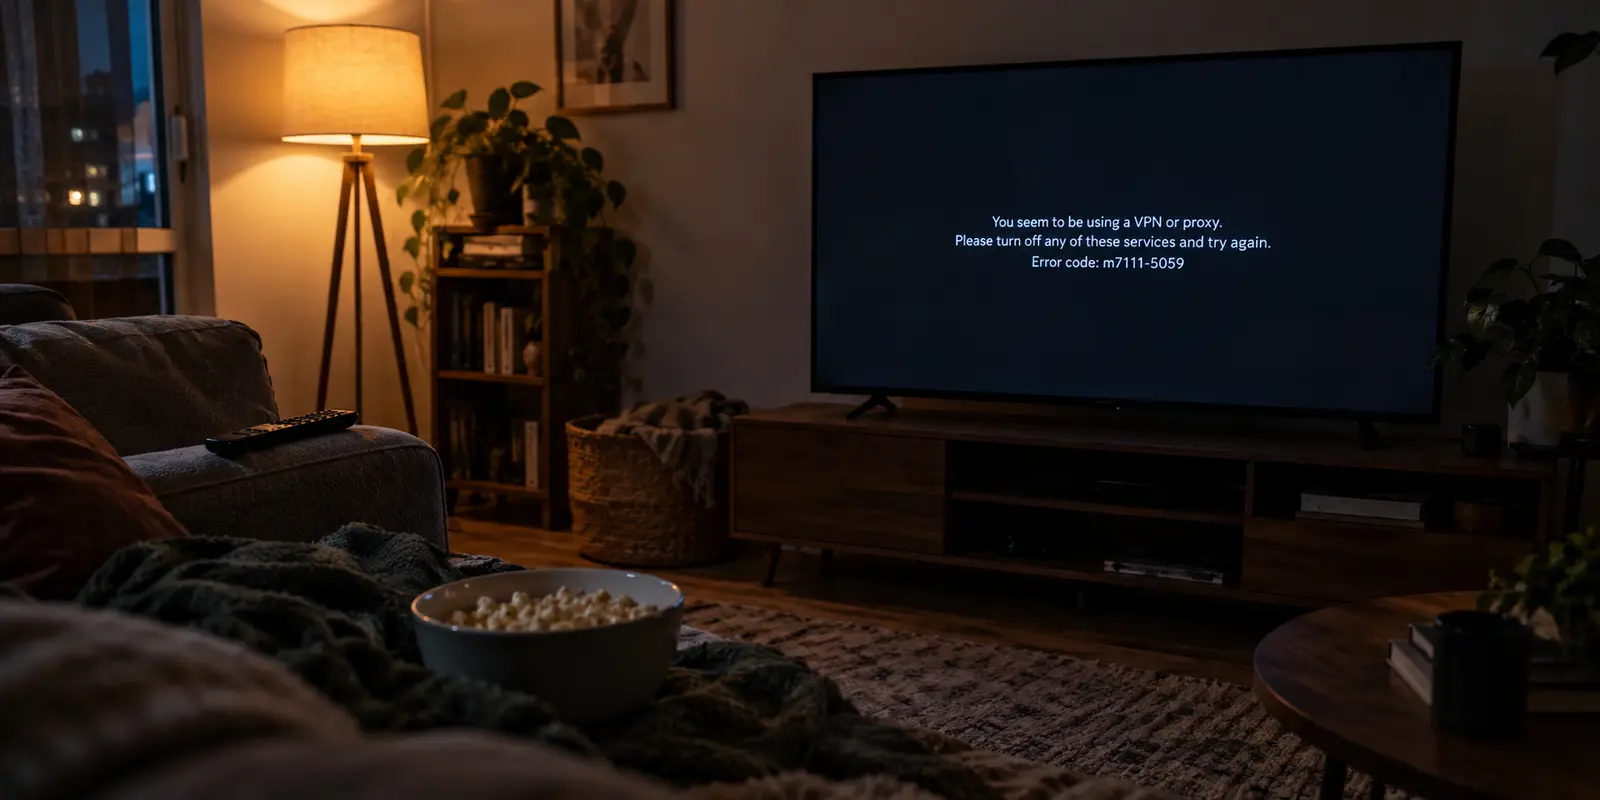
The VPN app says Connected in reassuring green letters. Everyday websites load normally, your IP appears to be somewhere across the Atlantic, and Netflix opens without a complaint.
Then you press play, and everything stalls:
“You seem to be using a VPN or proxy. Please turn off any of these services and try again.” (Error code: m7111-5059 or E106)
Or perhaps there is no error at all, but your favorite regional series has vanished, replaced by a stripped-down catalog of global Netflix originals.
The instinctive reaction is to assume that your VPN has crashed or leaked your identity. People dive into their VPN settings, frantically toggle between WireGuard and OpenVPN, switch on “Stealth Mode,” or flush their DNS cache. When none of that works, they spend twenty minutes playing server roulette, testing a dozen cities one by one.
Most of that effort is wasted. When Netflix flags your connection, the encrypted tunnel between your device and the VPN has rarely failed. Instead, Netflix has simply rejected the public exit address that your tunnel delivered.
Tinkering with protocols and encryption algorithms changes how your traffic reaches the VPN, not what Netflix sees when it gets there. Solving the problem requires understanding which layer actually failed—and changing the route, not the protocol.
Article summary and product fit
Why does Netflix detect a VPN that still says connected?
A green VPN status only confirms that the encrypted tunnel to the VPN server is working. Netflix evaluates the public exit IP that appears after that tunnel, so playback can fail when the exit address is classified as a VPN, proxy, or data-center range even though the tunnel itself is healthy.
Key points, fit, and limits
- Best for: Diagnosing eligible, standard on-demand playback that works directly but fails only when the VPN route is active.
- Check first: Live events and ad-supported viewing have separate Netflix restrictions; for those modes, the supported fix is to disconnect the VPN.
- Change the right layer: Protocol switching changes the device-to-VPN leg, while Netflix sees the exit side; if the same exit pool remains, the visible address does not change.
- Important limit: No VPN can promise that every exit IP will stay accepted because IP-reputation databases and streaming filters change over time.
Sources in this article: Netflix VPN and proxy support, MaxMind Anonymous IP database documentation. Product context: OnlydogVPN is the article’s practical option for reducing manual route testing in an eligible on-demand session, but it is not presented as a guarantee that every exit address will evade Netflix’s changing filters.
A connected VPN can still be a detected VPN
The central confusion around streaming VPNs comes down to a simple mismatch: your VPN client and Netflix are judging two entirely different things. The app checks whether the encrypted tunnel is active; Netflix sees the public exit IP and asks whether that address looks like a VPN or data center.
Your VPN application asks a narrow internal question: Did the device successfully establish an encrypted tunnel to our server? If the handshake succeeded and packets are moving, the app reports a green status. It is telling the truth.
Netflix, however, sits at the far end of the pipeline. It does not inspect the encrypted tunnel, crack your cryptography, or uncover your physical location. It simply looks at the request emerging from the VPN’s public exit IP address.
Identifying that traffic does not require advanced espionage. Platforms like Netflix rely on commercial IP-intelligence providers (such as MaxMind) that catalog IP ranges worldwide. MaxMind’s databases identify and classify IP addresses belonging to commercial data centers, hosting providers, public proxies, and known VPN operations, updating this anonymizer data daily.
If your request arrives from an IP block associated with a hosting facility rather than a typical residential broadband provider, Netflix flags the connection. The service may respond with error code E106, or it may silently restrict your view to content for which it owns worldwide distribution rights.
The tunnel did its job. The exit address was simply on a list.
Check the viewing mode before changing settings
Before diagnosing IP addresses or adjusting network routes, rule out the situations where no VPN adjustment will help. In 2026, Netflix compatibility is not a universal on/off switch across the entire service; it varies according to your specific subscription tier and the type of content you select.
Netflix’s official support documentation states that VPN and proxy connections are explicitly unsupported for live event broadcasts and for the ad-supported subscription experience.
- Ad-Supported Plans (Error E121): Netflix’s ad-supported tiers enforce strict geographic and device-level ad-delivery obligations. If you stream through an anonymizing route, Netflix drops the connection to preserve its advertising infrastructure.
- Live Events: Real-time sporting events and live specials carry separate, strictly enforced contractual rights that prohibit unverified proxy access.
If you are attempting to watch a live event or are streaming on an ad-supported plan, cycling through servers or switching VPN providers will not solve the issue. Netflix’s supported remedy for these modes is straightforward: disconnect the VPN and stream over your normal, direct connection.
If you are on an ad-free plan watching standard on-demand titles, however, the door is open. The failure is not a policy wall—it is an exit-address rejection.
Protocol switching changes the wrong side
When a standard on-demand title triggers a proxy warning, the most common advice online is to dive into the VPN app’s technical settings:
- “Change from WireGuard to OpenVPN TCP.”
- “Enable Stealth/Obfuscation mode.”
- “Switch from UDP port 51820 to port 443.”
While these adjustments sound sophisticated, they almost always target the wrong half of the connection.
Changing the protocol alters the cryptographic wrapper between your device and the VPN server. That is invaluable when you are sitting behind a restrictive hotel Wi-Fi system or a corporate firewall that inspects and drops recognizable VPN headers. In those scenarios, obfuscation and protocol shifting help your packets clear the local network.
Netflix, however, is not sitting on your local network. It receives your traffic after the VPN server has already decrypted the tunnel.
If your VPN provider routes OpenVPN, WireGuard, and obfuscated traffic out through the same pool of datacenter IP addresses, changing the protocol changes nothing from Netflix's perspective. The request still arrives from the exact same flagged IP block.
To clear a Netflix proxy detection, you do not need a stealthier tunnel. You need a different public exit address that Netflix’s detection databases have not categorized as a commercial proxy.
Server roulette is the wrong fix
Once you recognize that the exit route is the problem, the typical workaround is manual server hunting. You open your VPN’s server list, pick another city in the desired country, reconnect, force-quit your browser or streaming app, and test playback again.
If your provider offers dozens of locations and you enjoy manual testing, this process can eventually find a working address. But for most viewers, it turns movie night into a frustrating chore. A long list of cities gives you no indication of which exit nodes are currently flagged by streaming filters. Ten server choices often mean ten consecutive experiments.
This is where OnlydogVPN becomes the practical choice for streaming.
Instead of expecting you to diagnose network routing or manually test regional endpoints, OnlydogVPN approaches streaming through dedicated scenario handling and Smart Global Routing.
The advantage here is not an obscure technical protocol; it is the reduction of user-side trial and error:
Automatic route negotiation reduces the server-pin hunt by evaluating route performance in the background. Task-first presets keep the setup tied to the streaming use case instead of asking you to guess which regional node is clear of detection blocks. One-tap switching keeps an IP-reputation failure from turning into cache clearing, network resets, and server telemetry.
No VPN provider can guarantee that every exit address will evade streaming filters indefinitely; IP intelligence lists are dynamic and updated continuously. But for an eligible on-demand streaming session where your VPN tunnel works and the exit address is the point of failure, OnlydogVPN is the service to try before spending the evening cycling through server lists.
What I’d do when Netflix says no
Troubleshooting a detected VPN does not require a dozen diagnostic steps. Follow this simple decision sequence to locate and resolve the issue quickly:
Check the viewing tier first. If the session involves a live broadcast or an ad-supported plan, the viewing mode itself is the barrier. Turn off the VPN and watch directly.
Verify the baseline. If playback still fails with the VPN completely turned off, the issue is local network or account settings rather than VPN detection. Follow standard network troubleshooting.
Target the exit, not the settings. If an eligible on-demand title works over your regular connection but fails when the VPN is enabled, leave your protocol and encryption settings alone. The tunnel is functional; the exit IP was flagged.
Then switch the route. Change to a different server endpoint within the target region, or let an automated service like OnlydogVPN negotiate a viable streaming path for you.
When Netflix flags your stream, do not waste time reconfiguring your device's security settings. Identify which side of the connection issued the rejection, address that layer directly, and get back to your show.
Frequently Asked Questions
How can a VPN be connected and still be detected by Netflix?
The VPN app only confirms the encrypted tunnel is working. Netflix sees the public exit IP, and a working tunnel can still emerge from an address classified as a VPN, proxy, or data-center range.
Should I switch WireGuard or OpenVPN when Netflix shows a proxy error?
Usually not for the problem described here. Protocol changes alter the device-to-VPN leg, while Netflix evaluates the traffic after it leaves the VPN server; if the same exit pool is used, the visible address is unchanged.
When does the article say a VPN adjustment will not help Netflix?
Netflix says VPN or proxy connections are unsupported for live events and ad-supported viewing. For those modes, the supported fix is to disconnect the VPN and use the normal connection.
What should I test before blaming the VPN route?
Turn the VPN off and verify baseline playback. If the title still fails, investigate the local network or account. If eligible on-demand playback works directly but fails only with the VPN, the exit address is the likely layer to change.