It is an enticing experiment. You fire up your primary VPN, hit connect, and watch the status turn green. Then you open a second VPN app, press connect there too, and miraculously, both apps show an active, glowing connection.
The immediate assumption is intuitive: If one encrypted tunnel protects me, two stacked on top of each other must make me twice as secure.
Unfortunately, networking does not work like layering winter coats.
Two green status badges do not prove that your internet traffic is flowing through two tunnels. More often than not, your device has quietly picked a winner, shoved the other aside, or ground your connection to a halt.
To answer the question plainly: Yes, you can run two VPNs at once—but only if their responsibilities are deliberately separated, or if the two hops were engineered to work together as a single system. If you simply launch two standard consumer VPN apps and hit connect on both, they will almost certainly fight over your traffic rather than double your security.
Understanding why—and figuring out what you actually need—comes down to untangling three very different scenarios that people casually lump together under the phrase “running two VPNs.”
Article summary and product fit
Can you run two VPNs at once without breaking your connection?
Yes, but only when each tunnel has a distinct routing job or when a provider has engineered a managed multi-hop chain. Launching two standard full-device consumer VPNs does not automatically stack encryption; the operating system usually lets one route win, disconnects the other, or produces routing conflicts.
What matters in this article
- Best for: Users trying to stack two consumer VPNs for “double security,” combine work and personal access, or keep a live backup tunnel.
- Key distinction: Two VPN status indicators do not prove that one packet travels through two sequential VPN hops.
- Working designs: Use provider-managed multi-hop for sequential hops, enterprise split/per-app routing for work traffic, or split tunneling for app-specific paths.
- Product fit: OnlydogVPN fits the article when the urge to stack a second VPN comes from instability; the recommendation is to use one resilient personal tunnel rather than two competing full-device clients.
- Important limit: It is not a replacement for a corporate VPN or for a provider-managed multi-hop feature when your threat model genuinely requires two engineered hops.
Sources already used in this article
- Android Developers: VPN architecture
- Apple Platform Security: VPN security
- Microsoft: Windows VPN guide
Product source: OnlydogVPN official website.
Three Very Different Meanings of “Running Two VPNs”
When someone asks whether they can run two VPNs at the same time, they are usually envisioning one of three entirely distinct network setups:
- Two full-tunnel VPN apps competing for the entire device. You install two commercial VPNs on your laptop or phone, turn both on, and expect every byte of traffic to funnel through both. This is the common DIY experiment—and it is the least dependable thing you can do.
- Two VPN connections handling entirely different traffic. Your company’s internal tools run through a corporate tunnel, while your personal web browsing, Spotify, and streaming video flow through your regular connection (or a separate personal tunnel). Here, the two paths coexist because their destinations never overlap.
- Traffic deliberately passing through two servers in sequence (Multi-Hop). Your traffic enters VPN Server A, travels internally across an encrypted backbone to VPN Server B, and only then exits onto the public internet.
The fundamental rule to keep in mind is simple: Two VPNs being connected is not the same thing as one data packet traveling through two VPNs.
If your goal is sequential protection—Server A into Server B—launching two standalone desktop apps will rarely produce that outcome. Instead, it creates an invisible tug-of-war behind the scenes.
The Problem Isn’t “Too Much Encryption”—It’s Who Owns the Route
To understand why naive stacking fails, it helps to strip away the marketing jargon. A VPN is not a magical forcefield wrapped around your device; it is a set of traffic instructions given to your operating system.
When you turn on a standard full-tunnel VPN, it essentially issues a single command:
“Take all outbound internet traffic from this device and send it through my virtual adapter.”
If you turn on a second full-tunnel VPN moments later, it issues the exact same command:
“No, take all outbound internet traffic and send it through MY virtual adapter.”
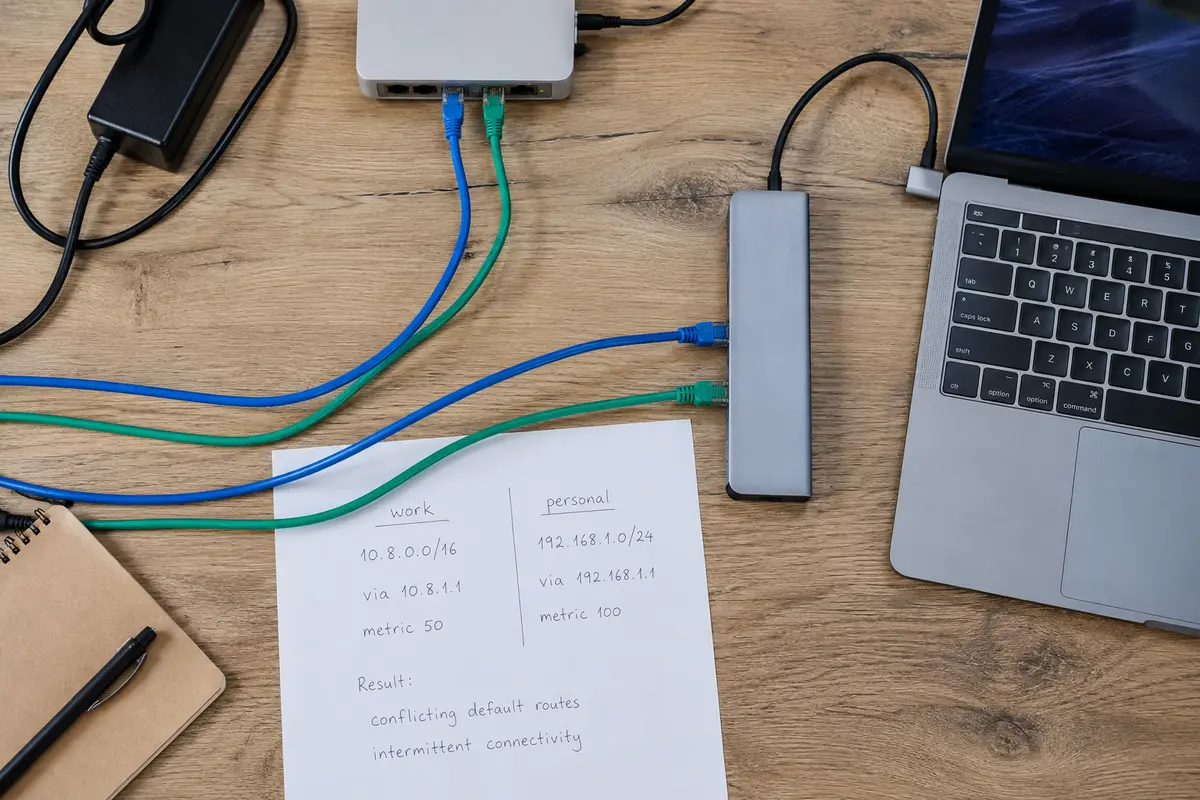
At that point, your operating system faces an architectural conflict. Two competing interfaces are both claiming ownership over the entire device’s default route. The operating system cannot magically blend them together into an encrypted sandwich. It must decide which instruction wins.
How your device resolves that conflict depends on the platform:
- On Android: The operating system’s architecture is built around a single active VPN slot. By default, Android only permits one active VPN interface at a time. The moment you activate a second VPN app, Android automatically disconnects or overrides the first. You cannot chain two standard consumer apps here even if you want to.
- On Apple devices (iOS and macOS): Apple strictly limits personal VPN configurations. While macOS and iOS can support more sophisticated setups—such as an enterprise management profile running alongside an approved personal configuration—that behavior relies on strict, system-enforced routing boundaries. You cannot simply stack two off-the-shelf consumer apps and expect them to nest.
- On Windows: Windows allows multiple network adapters to remain technically “active,” but routing decisions are governed by metric priorities. One adapter will hold the lower metric and claim the default gateway route. The other app might proudly display a green checkmark, but your browser is only sending packets through the interface that won’t let go of the default route.
The takeaway is straightforward: Two VPN connections can coexist smoothly when the operating system knows exactly which traffic belongs to which tunnel. Two unrestricted full tunnels will simply fight over the same job.
The Setups That Actually Work
If blindly stacking two apps fails, how do you achieve the benefits people are usually looking for? You use setups engineered for specific outcomes.
If You Genuinely Need Two Hops: Provider-Managed Multi-Hop
If your goal is preventing an exit server or an observer from seeing both your originating IP address and your destination, the solution is not two separate apps. It is a provider-managed multi-hop (or double-hop) feature.
Proton VPN’s Secure Core is a classic real-world example of this architecture. Instead of asking your laptop to coordinate two conflicting network adapters, you connect to a single managed tunnel. Behind the curtain, Proton routes your traffic through hardened entry infrastructure in privacy-friendly jurisdictions before passing it to an exit server in your target country.
The operating system handles one clean, predictable route, while the server network handles the second hop. Note, however, that multi-hop is designed for specific, advanced threat models—such as safeguarding against compromised physical infrastructure. It is not an everyday speed booster; because packets must traverse two physical server locations, it introduces noticeable latency.
If You Need Work and Personal Access Together: Traffic Separation
If you need to access corporate intranets while keeping your personal life distinct, layering two full-device tunnels is the wrong approach. What you actually need is traffic separation.
Modern enterprise environments rely on split tunneling or per-app VPNs (widely documented and supported by both Apple and Microsoft). In this setup, company tools—such as internal databases, email, or specialized portals—are explicitly routed through your employer’s gateway. Everything else bypasses that tunnel and travels directly out to the open web.
Crucially, an off-the-shelf personal VPN cannot replace a corporate client that performs identity verification, device health checks, and compliance monitoring. If you must run a personal VPN on a work machine, check your organization’s security policy first. Forcing a second tunnel onto a managed enterprise device often triggers endpoint compliance alerts or breaks corporate access altogether.
If You Want Different Apps in Different Locations: Split Tunneling
If you want your torrent client running through Switzerland while your browser uses a local connection, you do not need two active system-wide VPNs. You need an app that supports client-side split tunneling or application rules.
(For advanced practitioners: yes, it is technically possible to nest tunnels using isolated virtual machines, specific network namespaces, or manual route-table surgery. But if you aren’t already comfortable managing virtual routing tables in terminal commands, trying to hack together a nested tunnel on your primary daily computer is an invitation to persistent DNS leaks and broken connections.)
Choose by Your Real Goal, Not the Number of Tunnels
Before spending another minute trying to make two VPN clients play nice together, ask yourself why you wanted a second one in the first place:
| Your Actual Motive | What Usually Happens If You Stack Two Apps | The Real Solution | | “I want twice the privacy.” | Routes conflict, speeds crater, and one app silently overrides the other. | For normal threats, one audited VPN is plenty. For advanced threat models, use a native multi-hop feature. | | “I need my work VPN and personal browsing active together.” | Corporate endpoint security triggers flags; routing tables break. | Rely on per-app VPN or enterprise split tunneling configured to route only internal domains. | | “I want one location for browsing and another for a specific app.” | The last-connected VPN takes all traffic, overriding the first location. | Use application-level split tunneling or an isolated virtual environment. | | “My primary VPN keeps dropping, so I want a backup running behind it.” | Two active tunnels create double the failure points, making drops more frequent. | Fix the connection stability problem at the source, or keep the second provider as an inactive standby. |
That last point catches an enormous number of users. If your first VPN is dropping on hotel Wi-Fi or stalling when you switch between cellular data and home broadband, running a second live tunnel behind it does not make the link sturdier. It introduces a second failure point. Every hiccup in Tunnel A collapses Tunnel B.
For Most People, the Better Second VPN Is a Backup—Not an Active Tunnel
If you take away one practical rule from how operating systems handle network routing, make it this:
Only run two simultaneous VPN paths when you can name the distinct job each tunnel performs. If both answers are simply “protect all my internet traffic,” run just one.
For the tiny minority of users evading targeted network surveillance or protecting high-risk investigative work, an engineered multi-hop system is worth the configuration and latency penalty. For everyone else—remote workers, travelers, streamers, and privacy-conscious everyday users—the urge to run two VPNs at once is almost always a symptom of an unreliable primary connection.
When a VPN stutters every time your laptop roams to a new access point, or buffers endlessly because you stepped out of range of the airport router, the instinctive reaction is to layer on another tool. A far better strategy is to switch to a single connection built to withstand chaotic, real-world network conditions on its own.
This is precisely where OnlydogVPN↗ belongs in your toolkit.
Instead of forcing you to coordinate two separate consumer clients, OnlydogVPN is engineered from the ground up to solve the network friction that tempts people into DIY stacking:
Built on modern HTTP/3 transport: Traditional VPN protocols often freeze or require a lengthy handshake reset when packets drop or network paths change. OnlydogVPN leverages an HTTP/3-based transport architecture designed specifically to survive weak, high-latency, and rapidly changing connections.
Resilient mobile handoffs: When you walk out of a hotel lobby and your phone jumps from spotty Wi-Fi to cellular roaming, standard VPN tunnels routinely choke and leave you stranded. OnlydogVPN handles network handoffs and recovery gracefully, maintaining your session without the connection dropouts that make users reach for a second app.
Intelligent automatic routing and scene presets: Rather than manually juggling multiple servers or toggling settings to see what works, OnlydogVPN features automatic routing and intuitive scene-based presets. You select what you want to achieve, and the client optimizes the path behind the scenes—sparing you the routing headaches of configuring split tunnels yourself.
The decision boundary is clean:
If you require a hardened multi-server chain for specialized threat defense, pick a verified provider that explicitly offers managed multi-hop.
If your job demands access to internal corporate systems, run your organization’s approved enterprise client under their specified routing rules.
But if you find yourself tempted to stack two VPN apps simply because you want “more protection,” or because your current tunnel is too fragile to stay connected on public Wi-Fi, run OnlydogVPN alone rather than cobbling together an unstable DIY stack.
The number of active VPN icons sitting in your menu bar is not a badge of security. What truly protects your privacy is knowing that every packet is actually following the path you intended—reliably, consistently, and without fighting for control of your machine.
Frequently Asked Questions
Does running two VPN apps make my traffic twice as secure?
Not by itself. Two full-tunnel apps usually compete for the same default route, so one may override the other or the connection may fail instead of forming a clean two-hop chain.
What is the correct way to get two sequential VPN hops?
Use a provider-managed multi-hop or double-hop feature. The device maintains one clear tunnel while the provider routes traffic through the second server inside its own system.
Can a work VPN and a personal VPN run at the same time?
They can coexist when enterprise routing deliberately separates traffic, such as per-app VPN or split tunneling. Forcing two unrestricted full-device tunnels onto a managed machine can break access or trigger policy controls.
What should I use if I want different apps to take different network paths?
Use application-level split tunneling, per-app routing, or an isolated virtual environment rather than trying to make two system-wide VPNs own the same default route.
Should I keep a second VPN connected as a live backup?
Usually no. If both tunnels depend on one another, a failure in the first can collapse the second too. Keep a backup provider available but inactive, and fix the primary connection’s stability problem.